EU AI Act Compliance Enterprise: A Strategic Guide for Leaders
A definitive guide to EU AI Act compliance enterprise requirements. Navigate the complexities of the new AI legal framework Europe is imposing on global firms.
By Dakota Rea ·
EU AI Act Compliance Enterprise: A Strategic Guide for Leaders
> **Key Takeaways**
> - "Categorize every AI application into the four risk tiers defined by the Act to determine specific technical and legal obligations."
> - "Establish a centralized AI inventory that documents data provenance, model architecture, and training methodologies for regulatory scrutiny."
> - "Implement human-in-the-loop oversight mechanisms for all systems classified as high-risk to ensure ethical and operational safety."
> - "Update third-party vendor contracts to include specific AI compliance clauses and liability shifts for high-risk software components."
> - "Integrate continuous bias monitoring and accuracy testing into the DevOps lifecycle to maintain compliance throughout the model lifespan."
> **Dakota's Take**
>
> **"The EU AI Act is not a technical constraint; it is a structural stress test for modern leadership. Enterprises that view this as a bureaucratic hurdle rather than a strategic opportunity to build institutional trust will inevitably fall victim to the next wave of regulatory arbitrage and consumer backlash. Compliance is the new competitive moat."**
>
> *— Dakota Rea, AI Strategy Consultant*
According to **Gartner (2024)**, by 2026, organizations that prioritize AI transparency and trust will see a 50% increase in the adoption of their AI initiatives. Navigating **EU AI Act compliance enterprise** requirements has become the single most significant strategic hurdle for multinational corporations since the inception of the GDPR. As a Harvard Business School graduate and AI ethics consultant, I have observed that the most successful firms are not those trying to circumvent the rules, but those integrating them into their core value proposition. The **AI legal framework Europe** has established represents a global shift toward accountability that mirrors the historical transition toward environmental, social, and governance (ESG) standards. The complexity of these **AI regulatory requirements** necessitates a move away from siloed IT solutions toward a holistic, cross-functional strategy. In this guide, you'll discover a comprehensive roadmap for achieving **AI regulation compliance** while maintaining the agility required to compete in a rapidly evolving global market.
**Table of Contents**
1. The Strategic Context: From Innovation to Accountability
2. The Five-Step Framework for Enterprise AI Compliance
3. Critical Pitfalls: Where Enterprise Strategies Fail
4. Real-World Applications: Industry-Specific Compliance Models
5. The Road Ahead: 2025-2026 Trends in AI Governance
6. Frequently Asked Questions
The Strategic Context: From Innovation to Accountability
The era of "move fast and break things" has officially ended for artificial intelligence. In its place, the **EU AI regulation** has ushered in an era of principled innovation. A recent report from **McKinsey (2023)** suggests that generative AI could add up to $4.4 trillion annually to the global economy, but this value is contingent upon the stability of the regulatory environment. For the modern executive, **EU AI Act compliance enterprise** strategy is no longer a peripheral concern handled by the legal department; it is a fundamental component of enterprise risk management. Much like the Jeremy Bentham Scholar’s focus on the greatest good, we must now ask how our algorithms serve the collective interest without compromising individual rights.
The **AI legal framework Europe** has proposed is built on a risk-based approach. This means that the level of regulatory intervention is directly proportional to the potential harm an AI system could cause. For most enterprises, this requires a radical shift in how data is processed and how models are deployed. The **GDPR AI compliance** lessons of the last decade have taught us that reactive strategies are both costly and ineffective. Instead, a proactive stance on **AI regulatory requirements** allows a firm to build a "compliance-by-design" culture that reduces technical debt and enhances brand reputation.
To navigate this shift, leaders must understand three core pillars of the current regulatory climate:
- **Extraterritoriality**: Like GDPR, the EU AI Act applies to any entity placing AI systems on the EU market, regardless of where the company is headquartered.
- **Risk Tiering**: Systems are categorized as Prohibited, High-Risk, Limited Risk, or Minimal Risk, each with escalating layers of documentation and oversight.
- **Enforcement**: Penalties for non-compliance can reach up to €35 million or 7% of total global annual turnover, whichever is higher, making it a C-suite priority.
The Five-Step Framework for Enterprise AI Compliance
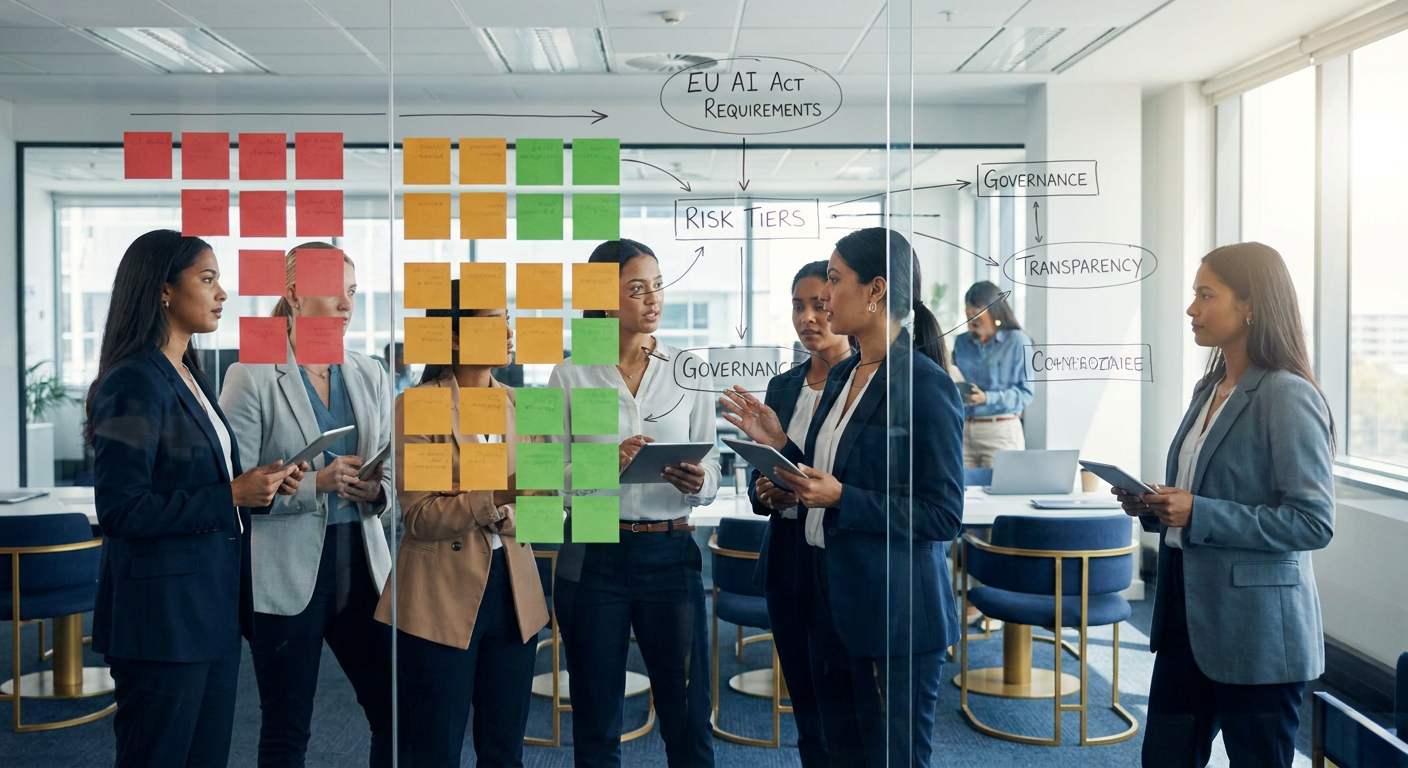
Achieving **EU AI Act compliance enterprise** status requires a structured methodology that bridges the gap between legal theory and technical execution. My consulting work with Fortune 500 companies has led to the development of this five-step framework, designed to ensure robust **AI regulation compliance** without stifling the creative potential of your data science teams.
### Step 1: Comprehensive AI Inventory and Risk Classification
You cannot govern what you cannot see. The first step in meeting **AI regulatory requirements** is to conduct a full audit of all AI systems currently in use or under development. This includes "shadow AI"—tools used by employees without official IT approval. Each system must be classified according to the EU’s risk tiers. High-risk systems, such as those used in recruitment, credit scoring, or critical infrastructure, will require the most intensive documentation and human oversight.
### Step 2: Gap Analysis and Technical Remediation
Once your systems are inventoried, compare your current technical stack against the requirements of the **AI legal framework Europe**. Are your models explainable? Do you have robust data governance protocols? For many, this step involves implementing **GDPR AI compliance** measures into the training data pipelines. You may need to retrain models if the underlying data was collected without sufficient transparency or if it exhibits prohibited biases.
### Step 3: Governance Structure and Human Oversight
The Act mandates that high-risk AI systems be designed so that they can be effectively overseen by natural persons. This is not just a technical requirement but an organizational one. You must define who is responsible for the AI’s output and establish clear protocols for when a human should intervene. This aligns with the MIT-certified ethics approach of ensuring that technology serves human agency rather than eroding it.
### Step 4: Documentation and Transparency Reporting
Transparency is the cornerstone of **EU AI regulation**. Enterprises must maintain detailed technical documentation that proves compliance. This includes descriptions of the model’s logic, the data used for training, and the results of risk assessments. For limited-risk systems, like chatbots, you must ensure that users are clearly informed they are interacting with an AI, maintaining the integrity of the human-machine interface.
### Step 5: Continuous Monitoring and Auditing
Compliance is a journey, not a destination. Establish a recurring audit cycle to monitor for model drift, new biases, or changes in the regulatory landscape. As the **EU AI Act compliance enterprise** requirements evolve, your governance framework must be flexible enough to adapt. This continuous loop ensures that your AI remains both legal and ethical as it scales across different jurisdictions.
Critical Pitfalls: Where Enterprise Strategies Fail
In my experience advising global firms, I have identified several recurring mistakes that lead to failed **AI regulation compliance** efforts. Avoiding these pitfalls is essential for maintaining operational continuity and avoiding the heavy fines associated with the **AI legal framework Europe**.
**The Silo Trap**: Many organizations treat **EU AI Act compliance enterprise** as a purely legal or purely technical issue. When legal teams write policies without understanding the technical limitations of neural networks, or when engineers build models without regulatory awareness, the result is a non-compliant product. Integration is key; you need a cross-functional "AI Ethics Board" that includes legal, technical, and strategic stakeholders.
**Ignoring Third-Party Risk**: A significant portion of an enterprise's AI footprint comes from third-party vendors. Assuming that a vendor is compliant because they are a large tech firm is a dangerous gamble. You must conduct due diligence on every vendor to ensure their tools meet **AI regulatory requirements**. Under the new rules, the "deployer" of an AI system often shares liability with the "provider."
**Underestimating the 'High-Risk' Definition**: Many companies mistakenly believe their AI applications are low-risk. However, the EU’s definition of "high-risk" is broad. For example, any AI used for employee performance monitoring or candidate filtering is likely to be classified as high-risk. Failing to identify these systems early leads to massive remediation costs later in the development cycle.
**Neglecting Data Provenance**: The **GDPR AI compliance** overlap is most apparent in data collection. If your AI is trained on data that violates privacy laws, the entire model may be deemed non-compliant. Enterprises often fail to track the lineage of their data, making it impossible to prove that the model was built on a legal and ethical foundation.
Real-World Applications: Industry-Specific Compliance Models
The impact of **EU AI Act compliance enterprise** requirements varies significantly across sectors. Understanding these nuances is vital for applying the **AI legal framework Europe** effectively within your specific business context.
**Financial Services**: In banking, AI is used for everything from fraud detection to credit scoring. Under the new **EU AI regulation**, credit scoring is explicitly labeled as high-risk. Banks must ensure their algorithms do not discriminate against protected groups. My approach involves implementing "Fairness Dashboards" that provide real-time metrics on algorithmic bias, ensuring that the **AI regulatory requirements** for non-discrimination are met while maintaining the predictive power of the models.
**Healthcare**: AI-driven diagnostics and patient monitoring systems are transformative but carry high stakes. Compliance here requires rigorous clinical validation and transparency regarding the model’s limitations. Healthcare providers must ensure that AI serves as a tool for clinicians, not a replacement for medical judgment, adhering to the human-oversight mandates of the Act. This is where the intersection of MIT-certified ethics and practical medicine becomes most critical.
**Manufacturing and Professional Services**: In manufacturing, AI optimizes supply chains and predictive maintenance. While these are often lower risk, the use of AI in HR for these global firms—such as resume screening—brings them into the high-risk category. Professional services firms using AI for legal research or document review must ensure **GDPR AI compliance** is maintained when handling sensitive client data, necessitating robust encryption and data anonymization techniques.
Across all these industries, the common thread is the need for a centralized governance platform. By standardizing the approach to **AI regulation compliance**, companies can reduce the overhead of managing multiple regulatory regimes and focus on the strategic deployment of AI to drive growth. This is the essence of the consulting work I lead: transforming regulatory complexity into operational excellence.
The Road Ahead: 2025-2026 Trends in AI Governance
As we look toward 2025 and 2026, the landscape of **EU AI Act compliance enterprise** will continue to shift. The **World Economic Forum (2024)** has highlighted AI-generated misinformation as a top global risk, which will likely lead to even stricter transparency requirements for generative models. We are moving toward a world where "Algorithmic Auditing" will be as commonplace as financial auditing.
One emerging trend is the rise of the **Chief AI Officer (CAIO)**. This role will be responsible for bridging the gap between innovation and the **AI legal framework Europe**. The CAIO will not only manage **AI regulatory requirements** but will also define the organization’s ethical stance on AI, ensuring that every deployment aligns with the company's long-term strategic goals. Furthermore, we expect to see the development of "Regulatory Sandboxes" across the EU, allowing companies to test innovative AI solutions in a controlled environment before full-scale deployment.
Another trend is the convergence of global standards. While the EU is the first to codify these rules, other jurisdictions—including the US and China—are developing their own frameworks. Enterprises that master **GDPR AI compliance** and the EU AI Act now will be well-positioned to lead in these markets. The ability to demonstrate **AI regulation compliance** will become a prerequisite for participating in global supply chains and securing international partnerships. The future belongs to those who view ethics as an asset, not a liability.
Frequently Asked Questions
### What is the primary goal of the EU AI Act for enterprises?
The primary goal is to ensure that AI systems used in the EU are safe, transparent, and under human control. It establishes a risk-based framework to protect fundamental rights while fostering innovation. For enterprises, it provides a clear legal roadmap for developing and deploying AI across the European market.
### How does EU AI Act compliance enterprise differ from GDPR?
While GDPR focuses on personal data protection, the EU AI Act focuses on the safety and ethical use of the AI models themselves. However, they overlap significantly, as model training often involves personal data. Both require rigorous documentation, transparency, and high standards of data governance to avoid significant fines.
### What happens if my company is based outside the EU?
The Act has extraterritorial reach. If your AI system's output is used within the EU or if you provide AI services to EU citizens, you must comply with the **AI regulatory requirements**. This makes it a global standard that multinational corporations must adopt regardless of their headquarters' location.
### Which AI systems are considered 'High-Risk' under the new law?
High-risk systems include those used in critical infrastructure, education, employment (recruitment/promotion), essential private and public services (credit scoring), law enforcement, and migration management. These systems face the strictest requirements for data quality, documentation, and human oversight to ensure they do not cause systemic harm or bias.
### When will the EU AI Act fully come into force?
The Act follows a phased implementation. Prohibited AI practices are banned within 6 months of entry into force, while requirements for General Purpose AI (GPAI) apply after 12 months. Most high-risk obligations will become mandatory within 24 to 36 months, making immediate strategic planning essential for enterprise readiness.
### How can a consultant help with AI regulation compliance?
An expert consultant provides the strategic bridge between technical teams and legal requirements. They help conduct risk assessments, design governance frameworks, and implement technical remediation. By aligning AI initiatives with the **AI legal framework Europe**, a consultant ensures that compliance becomes a driver of trust and market advantage.
Transform Your AI Strategy With Expert Guidance
Navigating the complexities of **EU AI Act compliance enterprise** requires more than just a checklist; it demands a fundamental rethinking of how your organization interacts with technology. My consulting practice specializes in helping Fortune 500 leaders turn these regulatory requirements into a strategic advantage. By visiting my /consulting page, you can learn how we integrate Harvard-level strategy with Oxford-trained ethics to future-proof your AI initiatives. Together, we can ensure your enterprise not only meets the **AI legal framework Europe** standards but leads the way in the new era of responsible innovation.